


Last updated: 12 September 2026. This article previously explained the NIS2 Directive and has been rewritten now that the Dutch Cybersecurity Act is in force.
Since 15 August 2026, the Dutch Cybersecurity Act (Cyberbeveiligingswet, or Cbw) has applied in the Netherlands. There is no general transition period: the obligations apply from day one. More than 8,000 Dutch organizations fall directly under the Act, and through their suppliers it reaches many more. This article explains what the Act is, who it applies to, what it requires and what you can do now.
What is the Dutch Cybersecurity Act?
The Cybersecurity Act is the Dutch implementation of the European NIS2 Directive. A directive does not apply directly: each EU member state turns it into its own national law. For organizations operating in the Netherlands, the rules of the Cbw apply. If you also operate in other EU countries, their national NIS2 laws may apply there as well.
The Cbw replaces the Dutch Network and Information Systems Security Act (Wbni), which since 2018 applied to a much smaller group of critical providers. The Dutch Senate approved the Act on 7 July 2026. At the same time, the Critical Entities Resilience Act (Wwke) came into force, covering the physical resilience of around 500 designated critical entities.
The goal of the Cbw is that organizations that matter to society and the economy secure their network and information systems better, report incidents quickly and can warn each other faster.
Who does the Act apply to?
The Act applies to organizations that provide essential or important services. Whether that includes yours depends on two things: the sector you operate in and the size of your organization. Note: you determine for yourself whether the Act applies to you. The government will not send you a letter; you have to assess it yourself.
Sectors
The Act follows the sectors of the NIS2 Directive, split into two groups.
Sectors of high criticality, such as energy, transport, banking, financial market infrastructure, healthcare, drinking water, wastewater, digital infrastructure, ICT service management (business-to-business), public administration and space.
Other critical sectors, such as postal and courier services, waste management, chemicals, food, manufacturing (including medical devices, electronics, machinery and vehicles), digital providers (such as online marketplaces and search engines) and research.
Size
As a rule of thumb, the Act applies to medium-sized and large organizations in these sectors: 50 or more employees, or more than €10 million in annual turnover or balance sheet total. Smaller organizations are generally out of scope. There are exceptions: some providers fall under the Act regardless of size, such as certain digital infrastructure providers like DNS service providers and trust service providers.
Essential or important
The Act distinguishes between essential and important entities. Large organizations in high-criticality sectors are usually essential; most other organizations in scope are important. The obligations are largely the same for both. The difference lies in supervision and maximum fines (see below).
Not sure? Use the official information and self-assessment from the Dutch government and the NCSC. Record your conclusion, even if it is that the Act does not apply to you, so you can later show how you reached it.
What does the Act require?
The Cbw has three core obligations: register, secure (the duty of care) and report. On top of that, the Act explicitly places responsibility with the board.
Registration
Organizations in scope must register in the entity register of the Dutch National Cyber Security Centre (NCSC). Registration has been mandatory since 15 August 2026. Once registered, you can use the services of the NCSC or your sector's CSIRT, such as threat intelligence and warnings.
Duty of care
The duty of care is the core of the Act. You take appropriate and proportionate measures to manage the risks to your network and information systems, and to limit the impact of incidents. "Appropriate" means: matched to your risks, your size and the state of the art.
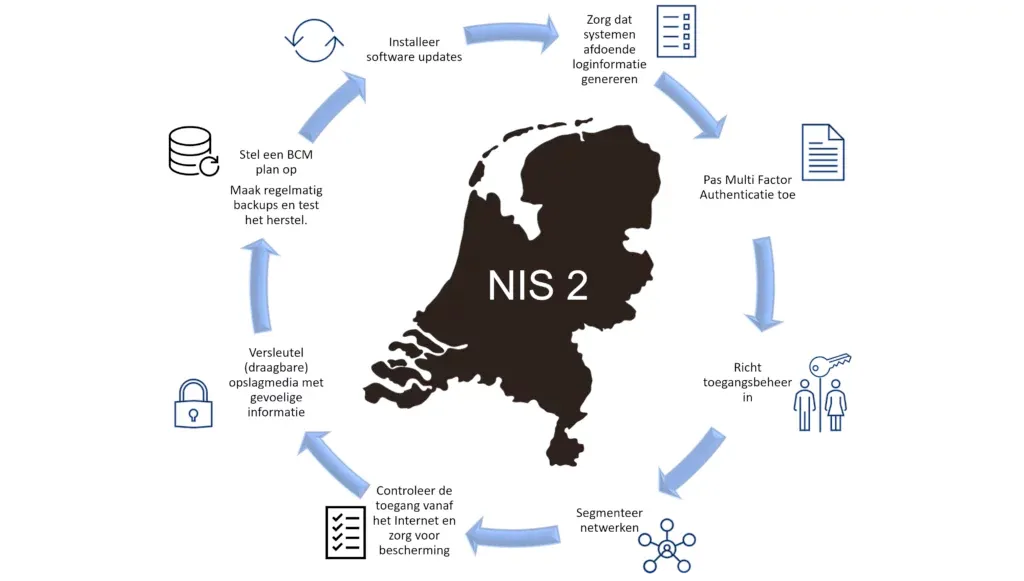
The NIS2 Directive lists a number of topics that must be covered in any case:
risk analysis and information security policies;
incident handling;
business continuity, such as backups and crisis management;
supply chain security;
security in the acquisition, development and maintenance of systems, including vulnerability handling;
assessing whether your measures are effective;
basic cyber hygiene and cybersecurity training;
the use of cryptography and encryption;
human resources security, access control and asset management;
multi-factor authentication and secured communications.
These measures are worked out further for the Netherlands in the Cybersecurity Decree (Cyberbeveiligingsbesluit).
Incident reporting
A significant incident, meaning one that seriously disrupts your services or can cause major damage, must be reported in stages:
Deadline | What |
|---|---|
Within 24 hours | Early warning via the NCSC's central reporting point |
Within 72 hours | Incident notification with an initial assessment of severity and impact |
Within 1 month | Final report with cause, impact and measures taken (or a progress report if the incident is ongoing) |
The deadlines run from the moment you become aware of the incident. Shorter deadlines apply to some organizations, such as trust service providers and organizations that also fall under DORA. If the incident also involves personal data, you must additionally report a data breach to the Dutch Data Protection Authority.
Board responsibility
Under the Cbw, cybersecurity is a board-level responsibility. The board approves the measures, oversees their implementation and is accountable when things go wrong. Board members must also have enough knowledge to assess cyber risks themselves, and must take training for this.
Supervision and penalties
Supervision is organized by sector, and each sector has its own supervisory authority. The Dutch Authority for Digital Infrastructure (RDI), for example, supervises the digital infrastructure sector. The NCSC is not a supervisor: it is the central reporting point and CSIRT, which helps organizations during incidents and warns them about threats.
What supervision looks like depends on your category:
Essential entity | Important entity | |
|---|---|---|
Type of supervision | Proactive: inspections, audits and requests for evidence, even without a specific reason | Reactive: after an incident, complaint or other signal |
Maximum fine | €10 million or 2% of worldwide annual turnover (whichever is higher) | €7 million or 1.4% of worldwide annual turnover (whichever is higher) |
Besides fines, supervisors can issue binding instructions and impose penalty payments, among other measures.
The lack of a transition period does not mean fines will be issued from day one. Supervisors are expected to focus on guidance in the early period. But if you cannot show after an incident that you took appropriate measures, you are in a weak position.
Even if you are not in scope: the supply chain
The Act applies directly to more than 8,000 organizations, but its reach is much wider. Supply chain security is part of the duty of care, so an organization under the Cbw must also manage the risks that come in through its suppliers: the IT service provider, the software vendor, the hosting company or the maintenance partner with access to systems.
As a supplier, you will notice this in practice:
you receive a supplier questionnaire about your information security;
new contracts and tenders include security requirements;
your customer asks for evidence, such as a certificate, a penetration test report or an overview of your vulnerability management;
you must quickly pass on incidents that affect your customer.
The Act does not oblige you as a supplier directly, but it does oblige your customer, who passes the requirements on. Being well prepared gives you an edge in winning and keeping business.
What should you do now? Six steps
Determine whether the Act applies to you. Look at your sector and size, use the official self-assessment and record your conclusion. Do you supply organizations under the Cbw? Then assume you will have to meet their requirements.
Register with the NCSC if you are in scope. This is already mandatory.
Map your risks. Which systems and services are critical, what can go wrong and what is the impact? Start with everything reachable from the internet, because that is where most attacks begin.
Take appropriate measures and document them. Use the duty of care topics as a checklist. Pay particular attention to vulnerability management: know which vulnerabilities you have, fix them in order of risk and document deliberate decisions.
Set up your reporting process. Who decides whether an incident is significant, who reports within 24 hours, and how do you combine that with a possible data breach notification? Practice it at least once.
Involve the board. Have the board approve the measures, schedule the board training and make cyber risk a standing agenda item.
Then make it a cycle. The duty of care is not a one-off project: systems change, new vulnerabilities appear every day, and you need to be able to show where you stand at any time.
How Catcher24 helps
No single tool makes you compliant on its own; the Act also requires policies, processes, and board involvement. Catcher24 helps with vulnerability management, and with proving it:
automated scans of your public servers, ports, services, and web applications for known vulnerabilities;
DNS and SSL/TLS checks;
prioritization and concrete recommendations in plain language;
reports with history: what was found, fixed, and consciously accepted.
That gives you the evidence your board, supervisor, customers, and insurer ask for. All scan and customer data is stored in the Netherlands.
Want to know more? Read how Catcher24 supports NIS2 or start a free 10-day trial.


Improve your cybersecurity today
Start your free trial now and discover what Catcher24 can do for your company. No credit card required, no installation. Just real insight into your real risks.

Similar posts


